Live event streams
You can stream events (sign-ups, logins, machine-to-machine tokens issued, and many more) in real-time, live as they happen in your Ory Network project, to your own infrastructure. Pipe those events into your own data warehouse, data lake, or flavor of choice, and use them to power your own analytics, dashboards, data science, and more.
Live event streams are available for Ory Network enterprise contracts. Talk to your account manager or reach out directly.
Event shape
Ory emits events for many different actions. All events abide by the same schema:
{
  "name": string,       // The unique name of the event (e.g., "IdentityCreated").
  "version": string,     // The numerical schema version of the event as a string.
  "timestamp": string,  // ISO 8601 formatted timestamp when the event occurred.
  "projectId": string,  // The ID of the Ory project the event belongs to.
  "eventAttributes": map<string, string> // Additional event-specific attributes.
}
Example:
{
  "name": "WebhookSucceeded",
  "version": "1",
  "timestamp": "2025-05-16 11:18:56",
  "eventAttributes": {
    "GeoLocationCity": "Munich",
    "TraceID": "4bf92f3577b34da6a3ce929d0e0e4736",
    "WebhookID": "",
    "WebhookTriggerID": "18093e08-0f72-445f-aacb-151fc777a232"
  }
}
Important:
- Per the JSON specification, ordering of keys in objects is not guaranteed and should not be relied upon.
- New keys can appear at any time, consumers should be designed to handle this.
- The exact content in the
eventAttributesfield is not documented and not considered stable. That means that no backwards compatibility guarantees are made for them.
If you intend to write a consumer that needs a detailed schema and stability guarantees about the eventAttributes field, please
open a support ticket.
Identity attributes
The IdentityID and ExternalID attributes are exceptions to the rule above. Their names and meaning are stable:
IdentityIDis the ID of the identity the event is about.ExternalIDis the identity's external ID. It's omitted when the identity doesn't have one. Use it to match events to user records in your own system without reading the identity from the Ory API.
Both attributes are set on IdentityCreated, IdentityUpdated, IdentityDeleted, LoginSucceeded, MFAChallengeIssued,
MFASucceeded, RegistrationSucceeded, RecoverySucceeded, RecoveryInitiatedByAdmin, SettingsSucceeded,
VerificationSucceeded, and all Session* events. LoginFailed, MFAFailed, RecoveryFailed, SettingsFailed, and
VerificationFailed carry them only when Ory identified the identity before the flow failed, for example on a wrong password.
IdentityDeleted carries the external ID the identity had when it was deleted.
ExternalID is delivered to your event stream only. Ory doesn't keep it in its own analytics.
Correlating events
All events that Ory emits while handling one request share the same TraceID attribute in eventAttributes. The value is the
W3C Trace Context trace ID of that request: 32 lowercase hexadecimal characters. Use it to
group the events of a single request, including events from different Ory services that took part in the same request, such as Ory
Identities completing a login and Ory OAuth2 accepting it.
A browser flow usually spans several requests, and each request has its own TraceID. To follow a self-service flow or a session
across requests, use the flow and session identifiers in eventAttributes.
The TraceID is absent when no trace ID is available and on events that summarize many requests, such as PermissionsChecked.
Treat the key as optional.
Identifying the initiator
Events that Ory emits while handling an authenticated admin API request say who made the request. This applies to the admin APIs of Ory Identities, Ory OAuth2, and Ory Permissions, whether you call them with a project API key or through the Ory Console, and to SCIM provisioning requests.
| Attribute | Description |
|---|---|
InitiatorType | The kind of initiator: api_key, console_user, or scim_client. |
InitiatorID | The ID of the API key, the ID of the Ory Console user, or the ID of the SCIM client. |
InitiatorName | The name of the API key. Only present when InitiatorType is api_key. |
Example: an identity deleted with a project API key.
{
  "name": "IdentityDeleted",
  "version": "1",
  "timestamp": "2026-10-01 11:18:56",
  "eventAttributes": {
    "InitiatorID": "874d556b-5be1-4478-8582-5b7607dbdde6",
    "InitiatorName": "CI pipeline",
    "InitiatorType": "api_key",
    "IdentityID": "d48cadd7-7b4a-491e-b9a8-21446868812e"
  }
}
InitiatorID identifies who performed the action. IdentityID identifies the identity the event is about. For console_user,
InitiatorID is the ID of the user's Ory Console account, not of an identity in your project.
The initiator attributes are absent on events from self-service flows and other public APIs, where the end user acts on their own account, and on events from work that Ory starts itself, such as sending courier messages. Treat the keys as optional.
Security context
An event stream can include the security context of the request behind each event. Use it to feed a security information and event management (SIEM) system. The option is off by default.
When the option is on, events caused by a request carry these keys in eventAttributes:
| Key | Value |
|---|---|
ClientIP | The IP address of the client that called Ory. |
UserAgent | The User-Agent header of the request, cut off after 512 bytes. |
RequestMethod | The HTTP method, for example POST. |
RequestHost | The host name the client called, for example auth.example.com. |
RequestPath | The URL path, for example /self-service/login. It never includes the query string. |
Keep in mind:
ClientIPandRequestHostdescribe whoever called Ory. When your backend calls Ory on behalf of a user, they describe your backend, unless it forwards the user's IP address in theTrue-Client-IPheader.- Requests that go through the Ory Proxy or Ory Tunnel report the
oryapis.comhost of your project. - Events that have no request behind them, such as events that summarize many requests, carry none of these keys.
- Ory doesn't store these values in its analytics.
To turn the option on, select Include security context when you create or edit an event stream in the Ory Console, or set
include_security_context to true through the Ory APIs. When you update a stream and omit the field, the stream keeps its
current setting. You can turn the option off at any time.
Event names
The following is a list of all events that are currently supported. The first column corresponds to the name field in an event.
New event names may be added in the future, in which case this list will be updated accordingly. These names are also the values
you can use in an event stream's event type filter.
Ory Identities
| Event | Description |
|---|---|
| IdentityCreated | A new identity (user or account) has been created. |
| IdentityDeleted | An identity has been deleted from the system. |
| IdentityUpdated | An existing identity's details have been modified or updated. The IdentityActive attribute in the event indicates the state of the active flag, as many SCIM providers deactivate users by setting active=false. |
| JsonnetMappingFailed | Mapping claims or attributes from an OIDC or SAML IdP failed. |
| LoginFailed | A user's login attempt has failed, possibly due to incorrect credentials. IdentityID is set when the attempt was matched to an identity. SelfServiceMethodUsed names the method that rejected the submission, and is empty when no method handled it, such as when the flow expired or the request did not address a method. |
| LoginInitiated | A new login flow has been created and basic validation passed. |
| LoginSucceeded | A user has logged into their account. SelfServiceMethodUsed names the method. SelfServiceSSOProviderUsed names the social sign-in or SAML provider. SelfServiceCodeChannelUsed is email or sms when a one-time code was used. |
| MFAChallengeIssued | A login flow asked a signed-in user for a second factor. MFAOfferedMethods lists the second factors the flow offers. A challenge with no MFASucceeded or MFAFailed for the same FlowID was never answered. |
| MFAFailed | A submission to a second-factor login flow failed, for example because of a wrong code or an expired flow. Emitted together with LoginFailed. |
| MFASucceeded | A user completed a second-factor login flow. SelfServiceMethodUsed names the second factor. Emitted together with LoginSucceeded. |
| RecoveryFailed | A password or account recovery attempt has failed. |
| RecoveryInitiatedByAdmin | An admin has initiated account recovery on behalf of a user. |
| RecoverySucceeded | A password or account recovery attempt has succeeded. |
| RegistrationFailed | A user's attempt to register has failed due to errors or invalid data. |
| RegistrationInitiated | A new registration flow has been created and basic validation passed. |
| RegistrationSucceeded | A user has registered and created an account. SelfServiceSSOProviderUsed names the social sign-in or SAML provider. SelfServiceCodeChannelUsed is email or sms when a one-time code was used. |
| SCIMGroupCreated | A new SCIM group has been created. Includes ScimClient attribute. |
| SCIMGroupDeleted | A SCIM group has been deleted. This event will also trigger IdentityUpdated events for all affected users. Includes ScimClient attribute. |
| SCIMGroupUpdated | A SCIM group has been updated. Modifying members of a group will also emit IdentityUpdated events for all affected users. Includes ScimClient attribute. |
| SCIMProvisioningError | An error occurred during the SCIM provisioning process, check the SCIMError Detail attribute for more information. |
| SessionChanged | A sessions details have been modified or updated. |
| SessionChecked | A check has been performed to verify the session's validity or status. |
| SessionIssued | A new session has been initiated for a user. |
| SessionLifespanExtended | The duration of a session has been extended, allowing the user to remain authenticated longer. |
| SessionRequiredAALRaised | A trusted producer, such as a login after web hook, raised the authenticator assurance level the session must reach. The user is sent to two-factor login, or to enrollment if they have no second factor. |
| SessionRevoked | A session has been explicitly terminated or invalidated. |
| SessionTokenizedAsJWT | A session has been converted into a JSON Web Token (JWT). |
| SettingsFailed | An attempt to change account or session settings has failed. |
| SettingsSucceeded | An attempt to change account or session settings has succeeded. |
| VerificationFailed | A user's identity verification attempt has failed. |
| VerificationSucceeded | A user's identity verification has succeeded. |
| WebhookDelivered | A webhook has been sent to the configured endpoint for processing. |
| WebhookFailed | A webhook delivery or processing has failed at the receiving endpoint. |
| WebhookSucceeded | A webhook has been processed and acknowledged by the receiving endpoint. |
| CourierMessageAbandoned | A courier message has been abandoned. |
| CourierMessageDispatched | A courier message has been dispatched. |
| DeviceAuthnKeyRegistered | A device authentication key enrollment was attempted. |
| DeviceAuthnKeyRemoved | A device authentication key removal was attempted. |
| DeviceAuthnKeyUsed | A device authentication key was used for step-up authentication. |
| DeviceAuthnKeySecretRotated | The PIN secret of a device authentication key was re-issued. |
| DeviceAuthnKeyLocked | A device authentication key was disabled after too many wrong PIN attempts. |
Ory OAuth2
| Event | Description |
|---|---|
| OAuth2LoginAccepted | A user's OAuth2 login has been accepted and the authentication process has succeeded. |
| OAuth2LoginRejected | A user's OAuth2 login attempt has been rejected due to invalid credentials or authorization issues. |
| OAuth2ConsentAccepted | The user has accepted the consent screen, granting requested permissions to the OAuth2 client. |
| OAuth2ConsentRejected | The user has rejected the consent screen, refusing to grant the requested permissions. |
| OAuth2ConsentRevoked | The user has revoked previously granted consent for an OAuth2 client, removing its permissions. |
| OAuth2ClientCreated | A new OAuth2 client (application) has been created and registered in the system. |
| OAuth2ClientDeleted | An OAuth2 client has been deleted from the system. |
| OAuth2ClientUpdated | An existing OAuth2 client's details have been updated or modified. |
| OAuth2AccessTokenIssued | An OAuth2 access token has been issued to a client or user. |
| OAuth2TokenExchangeError | An error occurred during the OAuth2 token exchange process, possibly due to invalid requests. |
| OAuth2AccessTokenInspected | An OAuth2 access token has been inspected to verify its validity or check its claims. |
| OAuth2AccessTokenRevoked | An OAuth2 access token has been revoked, invalidating it for future use. |
| OAuth2RefreshTokenIssued | A refresh token has been issued, allowing the client to obtain a new access token. |
| OAuth2RefreshTokenReuseDetected | A refresh token was presented again after it had already been rotated. The OAuth2RefreshTokenReuseKind attribute says whether it was a replay or a concurrent rotation. |
| OIDCIdentityTokenIssued | An OpenID Connect (OIDC) identity token has been issued to authenticate the user's identity. |
| OAuth2DeviceUserCodeAccepted | A user entered a valid user code in the OAuth2 device authorization flow. |
Ory Permissions
| Event | Description |
|---|---|
| RelationtuplesCreated | A new relation tuple has been created, representing a relationship between entities. |
| RelationtuplesDeleted | An existing relation tuple has been deleted, removing the relationship between entities. |
| RelationtuplesChanged | A relation tuple has been modified, indicating a change in the relationship between entities. |
| PermissionsExpanded | Permissions have been expanded, likely increasing access or privileges for certain users or entities. |
| PermissionsChecked | A permission check has been performed to verify if access is allowed for a given action or resource. |
Ory Network
| Event | Description |
|---|---|
| ProjectCreated | A project was created. |
| ProjectUpdated | A project was updated. |
| ProjectDeleted | A project was deleted. |
| StripeSubscriptionUpdated | A Stripe subscription was updated. |
| APIKeyCreated | An API key was created. |
| APIKeyDeleted | An API key was deleted. |
| CustomDomainCreated | A custom domain was created for a project. |
| CustomDomainDeleted | A custom domain was deleted from a project. |
| CustomDomainUpdated | A custom domain was updated. |
| ProjectMemberInviteCreated | An invitation for a project member was created. |
| ProjectMemberInviteAccepted | A project member invitation was accepted. |
| ProjectMemberInviteCancelled | A project member invitation was canceled. |
| ProjectMemberInviteDeclined | A project member invitation was declined. |
| ProjectMemberInviteDeleted | A project member invitation was deleted. |
| ProjectMemberRemoved | A member was removed from a project. |
| OrganizationOnboardingPortalLinkCreated | An onboarding link for an organization was created. |
| OrganizationOnboardingPortalLinkDeleted | An onboarding link for an organization was deleted. |
| OrganizationOnboardingPortalLinkUpdated | An onboarding link for an organization was updated. |
| SAMLProviderCreated | A SAML provider was created. |
| SAMLProviderDeleted | A SAML provider was deleted. |
| SAMLProviderUpdated | A SAML provider was updated. |
| OIDCProviderCreated | An OIDC provider was created. |
| OIDCProviderDeleted | An OIDC provider was deleted. |
| OIDCProviderUpdated | An OIDC provider was updated. |
| SCIMClientCreated | A SCIM client was created. |
| SCIMClientDeleted | A SCIM client was deleted. |
| SCIMClientUpdated | A SCIM client was updated. |
Delivery guarantees
- Possible duplicates: There might be duplicates in the event stream. While rare (typically caused by retries because of network issues), consumers should be prepared to deal with them, for example by implementing deduplication logic.
- Best-effort delivery: Event delivery is best-effort. While most events are delivered reliably, events may be lost under adverse conditions (for example, system crashes during request processing). Delivery is not guaranteed to be "at-least-once".
- No delivery latency SLA: Ory does not offer a Service Level Agreement (SLA) for event delivery duration (the time between an event occurring and it appearing in your consumer or the Ory Console UI). However, typical delivery times are observed to be less than 5 seconds.
- No ordering guarantees: Events may arrive in any order, both within a request and across different requests.
Stronger guarantees can be implemented for your use case if needed, in this case please open a support ticket.
Configure event streams
Is your workload not running on AWS or you don't want to use SNS? Reach out to discuss your requirements! Event streams can be implemented for any data warehouse, data lake, or equivalent solution.
Stream to HTTPS endpoint
To stream events to an HTTPS endpoint, provide the URL of the endpoint when configuring the event stream:
- Ory Console
- Ory CLI
-
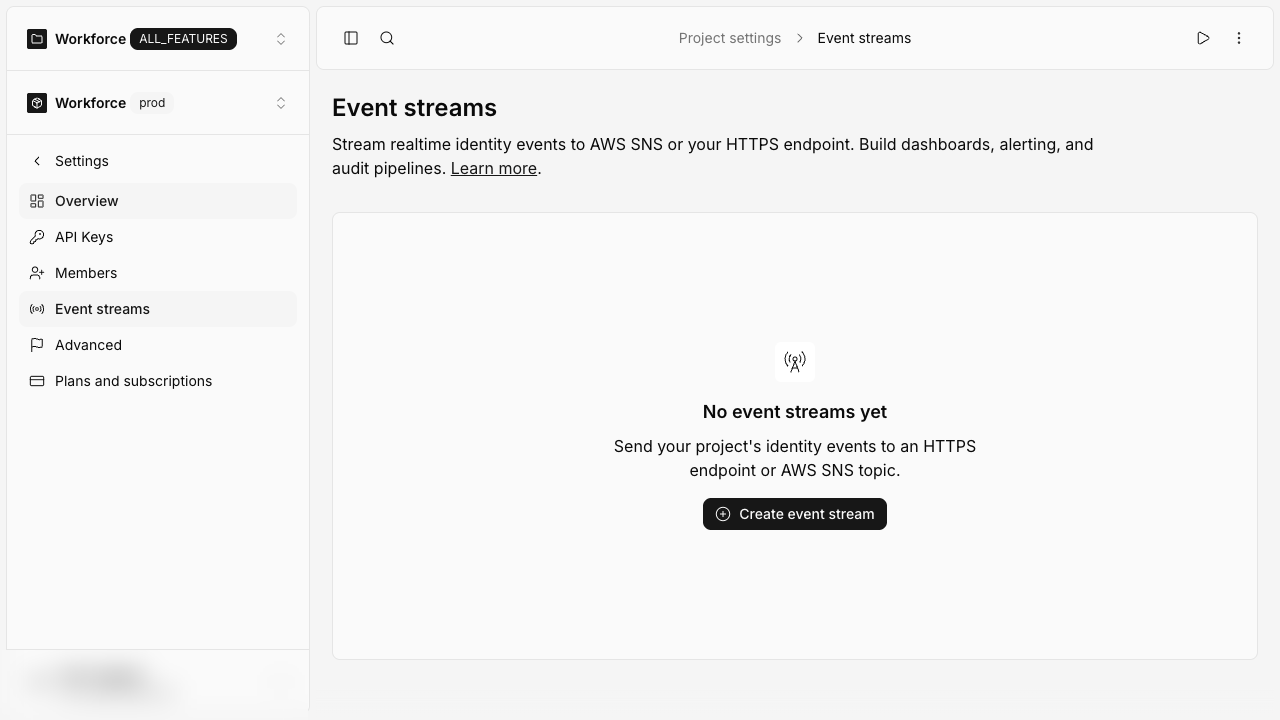
Go to your project in the Ory Console.
-
Click Project settings in the top navigation bar.
-
Click Event streams in the left sidebar.
-
Click Create new Event Stream.
-
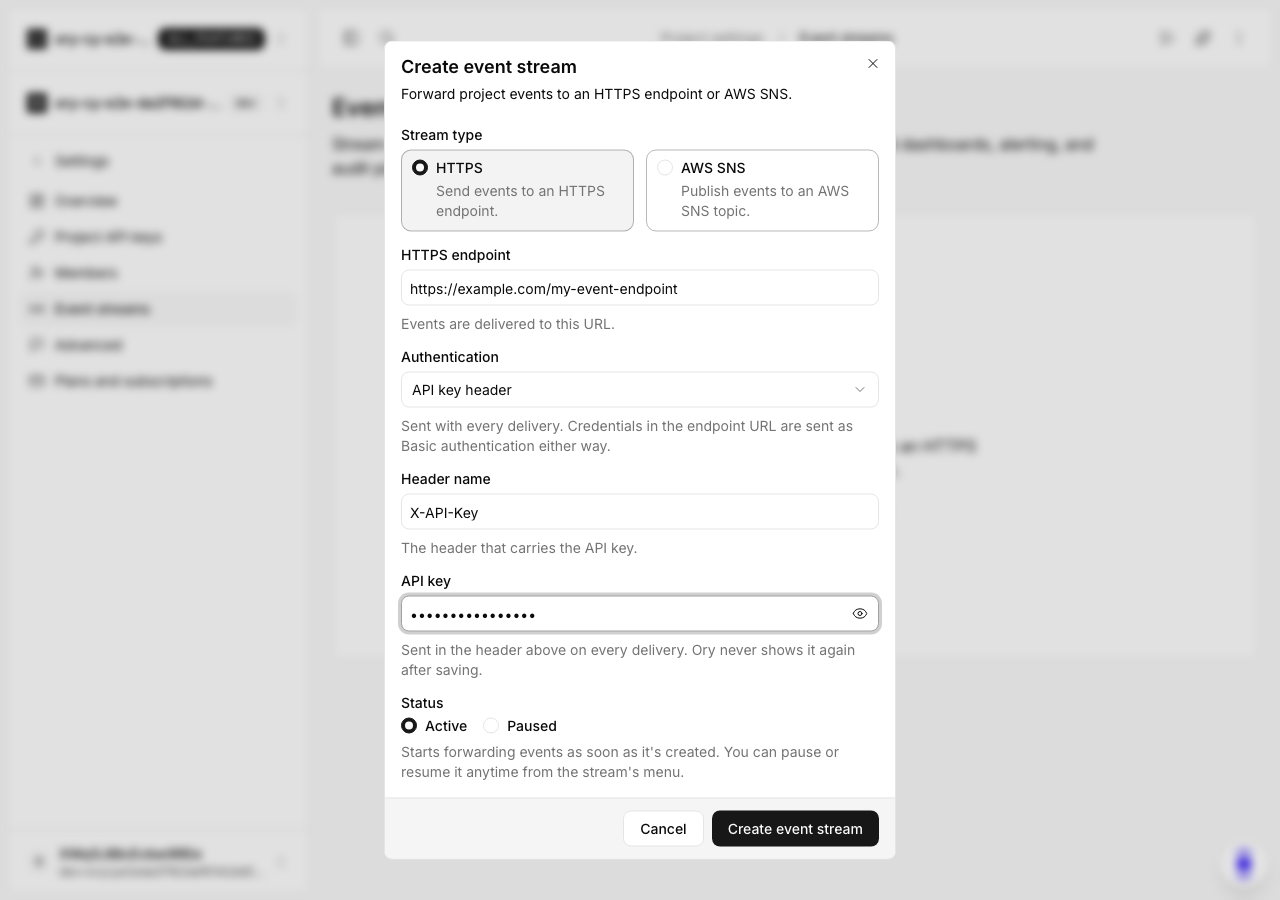
In the Create new Event Stream dialog:
-
Event Stream Type — Select HTTPS.
-
HTTPS endpoint — Enter the URL of your endpoint, for example
https://example.com/my-event-endpoint. -
Authentication — Optional. Select how Ory authenticates each delivery. For API key header, enter the Header name your endpoint expects, for example
X-API-Key, and the API key. For Bearer token, enter the token. See Authenticate deliveries.
-
-
Click Create. The new stream appears in the event streams table.
ory create event-stream
  --project "$YOUR_PROJECT_ID" \
  --type https \
  --https-endpoint https://example.com/my-event-endpoint
Unencrypted HTTP endpoints are not supported. Your endpoint must be able to handle POST requests with a JSON body, and respond with a 2xx status code to acknowledge successful processing of the event. HTTP redirects are not followed and are treated as delivery failures.
Your endpoint should support HTTP/2. HTTP/2 multiplexing lets Ory deliver many events concurrently over a single connection, which makes event delivery more efficient.
Authenticate deliveries
Ory can authenticate each delivery to your endpoint. You configure authentication in the Ory Console when you create or edit a stream, or through the Ory API and the Ory SDKs. The Ory CLI sets only the endpoint URL. Pick the scheme your endpoint or API gateway expects:
- Basic authentication: include the credentials in the endpoint URL, for example
https://username:[email protected]/my-event-endpoint. Ory sends them in theAuthorizationheader. - API key header: set
https_auth_typetoapi_key, name the header inhttps_auth_header_name(for examplex-api-key), and provide the key inhttps_auth_secret. Ory sends the key in that header on every delivery. The header name can be at most 128 bytes. It cannot be a header Ory sets itself, such asContent-Type,User-Agent, or anyOry-*orX-Ory-*header, or a connection-specific header that HTTP/2 does not allow, such asConnection,Keep-Alive,Upgrade, orTE. The key can be at most 4096 bytes. You can combine an API key header with credentials in the URL unless the header isAuthorization. - Bearer token: set
https_auth_typetobearerand provide the token, at most 4096 bytes, inhttps_auth_secret. Ory sends it asAuthorization: Bearer <token>. Bearer authentication cannot be combined with credentials in the URL, because both use theAuthorizationheader.
For example, to create a stream that authenticates with an API key:
{
  "type": "https",
  "https_endpoint": "https://example.com/my-event-endpoint",
  "https_auth_type": "api_key",
  "https_auth_header_name": "x-api-key",
  "https_auth_secret": "<your API key>"
}
Ory never returns a secret: API responses show xxxxx in place of https_auth_secret, and mask the credentials in
https_endpoint. When you update a stream, omit a secret to keep the stored value, send a new value to rotate it, or set
https_auth_type to none to remove authentication.
A stored https_auth_secret is only sent to the endpoint and under the scheme it was set for. Changing https_endpoint, even
only its path, or switching between api_key and bearer, requires https_auth_secret in the same update. Ory rejects the
update otherwise, before it sends any request to the endpoint.
In the Ory Console, the Edit event stream dialog shows a stored API key or bearer token as an empty, locked field. Leave it as it is to keep the secret, or click Change next to it and enter a new value to rotate it. Selecting a different Authentication scheme or entering a new HTTPS endpoint unlocks the field, and you must enter the secret again. Select None to remove authentication.
Ory sends the connectivity test message with the same authentication as regular deliveries, so an endpoint that rejects unauthenticated requests still passes the check when you create or update the stream.
Stream to AWS SNS
Configuring AWS SNS as an event stream destination is easy and requires no exchange of confidential information.
- Create an AWS SNS topic, and record its ARN (Amazon Resource Name), for example:
arn:aws:sns:us-east-1:123456789012:my-topic
- Create an AWS IAM role with publish permission to that topic. Sample IAM policy:
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "OryNetworkEventStreamPublish",
      "Effect": "Allow",
      "Action": ["sns:Publish"],
      "Resource": ["<YOUR TOPIC ARN>"]
    }
  ]
}
Record the ARN of the IAM role you created, for example:
arn:aws:iam::123456789012:role/ory-network-event-streamer
- Attach the following trust policy to the IAM role you created in step 2, replacing
<YOUR PROJECT UUID>with your project ID:
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Effect": "Allow",
      "Principal": {
        "AWS": "601538168777"
      },
      "Action": "sts:AssumeRole",
      "Condition": {
        "StringEquals": {
          "sts:ExternalId": "<YOUR PROJECT UUID>"
        }
      }
    }
  ]
}
This allows Ory Network to assume the role in your AWS account, and publish to your SNS topic.
-
Configure the event stream, replacing the ARNs with those recorded in steps 1 and 2:
- Ory Console
- Ory CLI
a. Go to your project in the Ory Console.
b. Click Project settings in the top navigation bar.
c. Click Event streams in the left sidebar.
d. Click Create new Event Stream.
e. In the Create new Event Stream dialog:
-
Event Stream Type — Select AWS SNS.
-
Role ARN — Paste the IAM role ARN from step 2.
-
Topic ARN — Paste the SNS topic ARN from step 1.
f. Click Create. The new stream appears in the event streams table.
https://console.ory.com/projects/b3b748e5-7ddc-4860-a672-2436a877dc93/settings/event-streams ory create event-stream--project "$YOUR_PROJECT_ID" \--type sns \--aws-sns-topic-arn "$YOUR_TOPIC_ARN" \--aws-iam-role-arn "$YOUR_IAM_ROLE_ARN"
-
You are now ready to receive events in your AWS SNS topic!
For development purposes, you can subscribe an email address to your topic, and receive events via email. For production use, subscribe AWS SQS, AWS Kinesis Data Firehose, or any other AWS service that can consume events from an SNS topic. Check the AWS documentation for ideas.
Filter events
By default, an event stream delivers every event of your project. To deliver only some of them, set the stream's event_types to
the events it should deliver. Each entry is either an exact name from the event names tables or a pattern that
matches several of them. Events that match no entry are not delivered to that stream. Filtering one stream has no effect on your
other event streams.
In a pattern, * matches any sequence of characters, and no other wildcard is supported. For example, Session* selects every
session event, OAuth2* selects every OAuth2 event, and *Failed selects every failure event across all products.
Set the filter when you create a stream, or change it on an existing stream:
- API
Updating an event stream is a partial update, so send only event_types to change the filter and keep every other setting:
curl --location --request PUT "https://api.console.ory.com/projects/${ORY_PROJECT_ID}/eventstreams/${EVENT_STREAM_ID}" \
  --header "Content-Type: application/json" \
  --header "Authorization: Bearer ${WORKSPACE_API_KEY}" \
  --data '{
    "event_types": ["*Failed", "Session*", "OAuth2AccessTokenRevoked"]
  }' | jq
The response contains the stored filter, sorted and without duplicates.
Every entry must match at least one event name from the tables above. A request with an unknown name, a pattern that matches no
event, or a pattern that uses a wildcard other than * fails with a 400 Bad Request error that names the invalid entry. The
combined length of all entries in a filter cannot exceed twice the combined length of all event names in the tables above.
- To keep the current filter when you update a stream, for example to pause or resume it, omit
event_types. - To remove the filter so that the stream delivers every event again, send an empty list:
"event_types": []. - An exact name matches only that event. A stream filtered by names alone does not receive event types that Ory adds later until you add them to its filter.
- A pattern also matches event types that Ory adds later when their names match. Those events are delivered and count toward your event stream usage like any other delivered event.
- The filter is applied when an event is delivered. If you change the filter of a paused stream, the new filter also applies to the events that were buffered while it was paused.
- Events that a filter excludes do not count toward your event stream usage.
Pause and resume event streams
You can pause an event stream to temporarily stop delivering events to its destination without deleting the stream or its configuration. Pause a stream while its destination is undergoing maintenance, is misconfigured, or is being replaced, then resume it to continue delivery. Pausing one event stream has no effect on your other event streams.
Pause or resume a stream
- Go to your project in the Ory Console.
- Click Project settings in the top navigation bar.
- Click Event streams in the left sidebar. The Status column shows whether each stream is Active or Paused.
- Open the ⋯ menu next to the stream and click Pause or Resume.
You can also change the status through the Ory APIs. Updating an event stream is a partial update: send only the status field
(active or paused) and every other setting keeps its current value. This is the recommended way to pause or resume a stream,
because resubmitting the destination is not required.
When you resume a stream, Ory first verifies that the destination is reachable, the same check that runs when you create or update a stream.
Create a stream as paused
When you create a stream in the Ory Console, set Status to Paused to save it without starting delivery. This is useful when you want to configure a stream before its destination is ready. Resume it later from the stream's ⋯ menu.
What happens to events while a stream is paused
In short: while a stream is paused Ory keeps receiving your project's events and buffers them for that stream for up to 7 days. Resume within that window and Ory delivers everything that was buffered while the stream was paused.
In more detail:
- Pausing only stops delivery. Ory keeps collecting the events your project produces and holds them in an internal buffer dedicated to that stream. Nothing is delivered to your destination while the stream is paused.
- Buffered events are retained for up to 7 days. When you resume the stream, Ory delivers the buffered backlog first and then continues with new events. This catch-up delivery follows the same guarantees as normal delivery: best-effort, possibly out of order, and possibly with duplicates.
- Events that have been buffered for longer than 7 days are permanently discarded, whether or not you resume the stream. A stream that stays paused for more than 7 days keeps only the most recent 7 days of events; anything older is lost.
- Buffered events go through the stream's event type filter when they are delivered, so a filter you change while the stream is paused applies to them too.
Pausing one stream does not affect your other event streams, and does not affect events available elsewhere in Ory, such as the project's activity view in the Ory Console.
Pausing buffers events for up to 7 days. If a stream stays paused for longer, the oldest events are permanently lost. Resume the stream within 7 days to receive everything you missed.
Retry policy
If your event stream destination is unavailable or misconfigured, Ory Network will retry sending the event multiple times with an exponential backoff between attempts.